Web applications
Examine sign-in, user permissions, inputs, uploads and business rules using agreed environments and test accounts.
EXP Frontier
Find the exposure.
Verify the fix.
Understand what an attacker could reach. Give your team clear priorities, reviewed evidence and a practical next step.
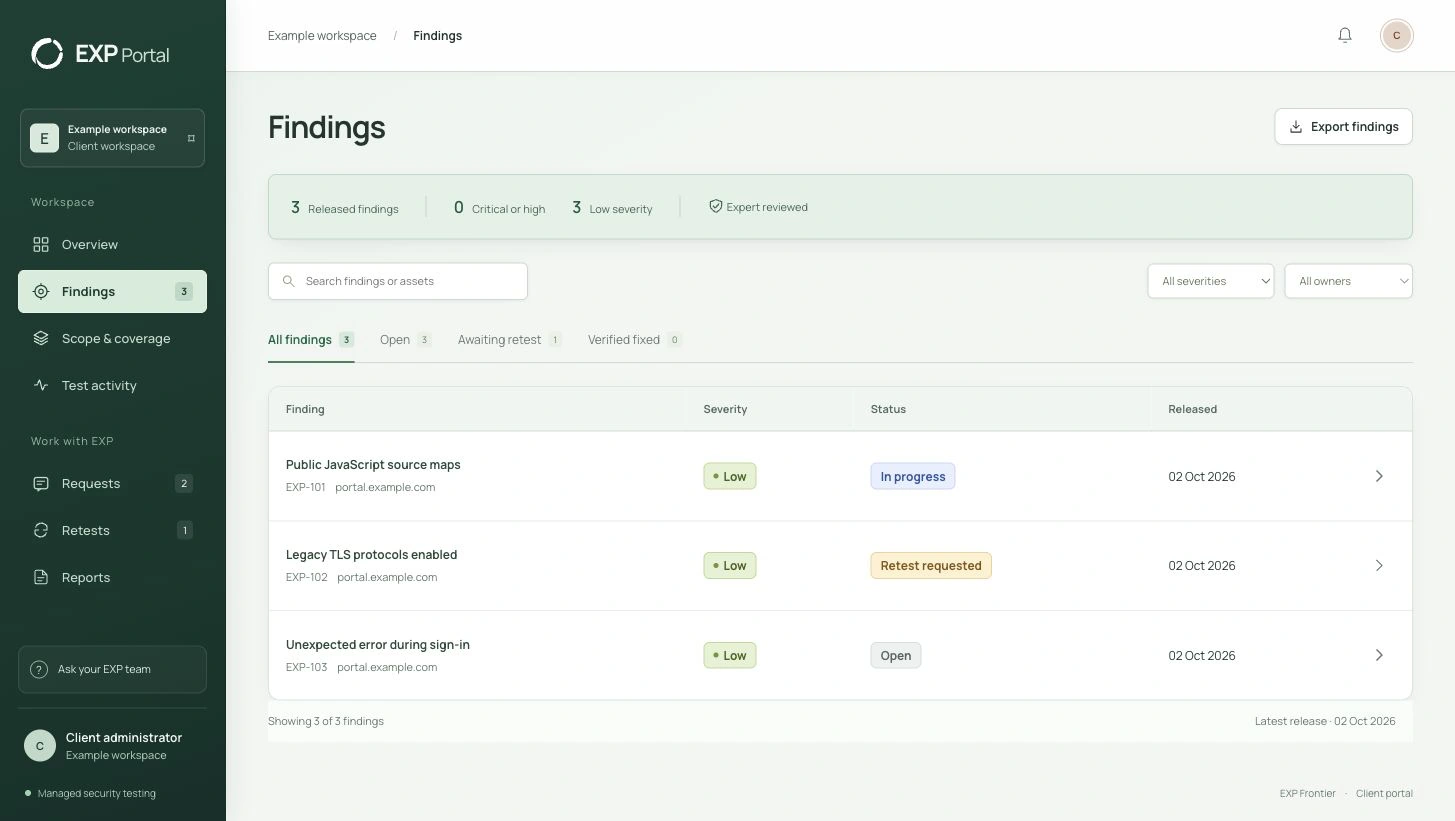
Scope, evidence and progress in one workspace.
A public website, an authenticated application or the APIs behind a customer journey. We agree the boundaries and test the paths that matter to your business.
Examine sign-in, user permissions, inputs, uploads and business rules using agreed environments and test accounts.
Check the requests behind the interface, including access to records, sensitive responses and protected actions.
Review agreed domains and public assets for revealing files, configuration weaknesses and known vulnerable software.
AI helps investigate potential weaknesses and organise evidence. EXP reviews the findings, explains their impact and gives your team a useful recommendation.
Agree the assets, test accounts, permitted techniques, exclusions and timing before testing begins.
Test the agreed journeys, validate evidence and prioritise findings by exploitability and business impact.
Your team deploys the change. EXP retests the issue within the agreed allowance and records the reviewed result.
EXP Portal brings findings, evidence, requests and retests together. Share a report with the people who need an answer, and keep the detailed next steps with the people doing the work.
Explore EXP PortalThe assets, access, test method, delivery window, report and retest allowance. Repeat assessments and additional applications can be included. A portal example does not establish your package or service level.
An assessment records what was tested at a particular time. Any recurring checks have an agreed cadence. Automated checks, staffed incident response and restoration commitments are separate services with their own scope and terms.
Penetration testing usually supports your IT team or developer, who deploys the changes. For a supported WordPress website, our done-for-you security service gives EXP responsibility for implementation within the agreed website scope.
Tell us about the application, the people using it and the decision your assessment needs to support.